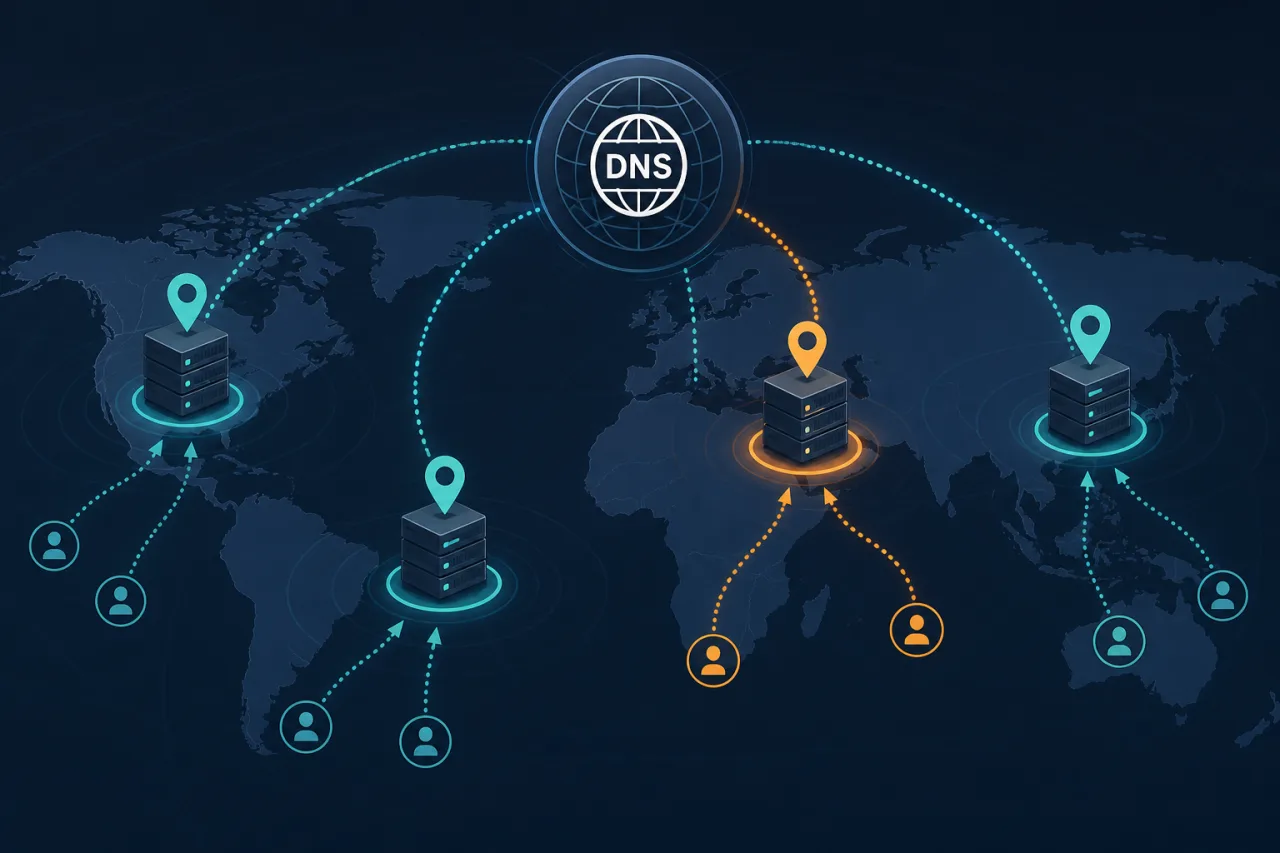
What Is Global Server Load Balancing?
Traditional load balancers distribute traffic across servers in a single datacenter. Global server load balancing (GSLB) does the same thing across geographically distributed datacenters or cloud regions.
The goal is threefold: reduce latency by routing users to the nearest healthy origin, survive regional outages without manual intervention, and distribute load so no single region becomes a bottleneck.
GSLB operates primarily at the DNS layer. When a user's resolver queries your domain, the GSLB-aware nameserver returns the IP address of the most appropriate endpoint — based on the requester's location, the health of each origin, or both.
How Anycast DNS Works
Anycast is a routing scheme where multiple geographically distributed hosts share the same IP address. BGP then routes each incoming packet to the topologically nearest node advertising that prefix.
This is different from unicast, where one IP maps to one host. With anycast:
- A resolver in Tokyo hits a Tokyo PoP.
- A resolver in Frankfurt hits a Frankfurt PoP.
- Both queried the same IP address.
Anycast is what makes large public DNS resolvers like 1.1.1.1 and 8.8.8.8 fast globally. The same principle applies when you run your own authoritative nameservers or use a DNS provider that anycast-distributes its infrastructure.
Important distinction: Anycast DNS and GSLB are not the same thing. Anycast gets the DNS query to the nearest nameserver quickly. GSLB is the logic inside that nameserver deciding which origin IP to return.
GSLB Routing Methods
Most GSLB implementations support several routing policies. Choose based on your actual requirements:
Geographic / Geolocation Routing
Return the IP of the origin closest to the resolver's IP. Works well for latency reduction. Watch out for resolver IP ≠ user IP situations (EDNS Client Subnet helps here, but adoption is partial).
Latency-Based Routing
Some providers actively probe origins and route to the one with the lowest measured latency from each region. More accurate than pure geolocation but requires ongoing measurement infrastructure.
Weighted Routing
Split traffic by percentage. Useful for canary deployments or gradual region migrations. A 90/10 weight between us-east and eu-west keeps most traffic on the proven region while you validate the new one.
Failover Routing
Designate a primary and one or more secondaries. Traffic shifts automatically when health checks fail. This is the most common GSLB use case and the easiest to reason about.
Health Checks Are the Critical Dependency
GSLB is only as good as its health check data. If a region goes down but the GSLB doesn't know, it keeps sending traffic into a black hole.
Key considerations for health checks:
- Check from multiple vantage points. A health check from a single location can miss regional connectivity failures that affect real users.
- Check the right thing. An HTTP 200 from your load balancer's default page doesn't prove your application stack is healthy. Hit a real endpoint that exercises your DB connection or cache.
- Set appropriate thresholds. One failed check shouldn't trigger failover — you want 2–3 consecutive failures to avoid flapping on transient errors.
- TTL alignment. Your DNS TTL must be low enough that clients pick up the failover record before the health check timeout becomes user-visible. 30–60 seconds is a common target for critical services.
This is where external uptime monitoring complements your GSLB health checks. Services like Pingy run checks from distributed locations independently of your infrastructure — so if your GSLB health check agent itself has a problem, you still get an alert. Treat them as independent confirmation, not duplication.
Setting Up GSLB: A Practical Checklist
- Choose a DNS provider with native GSLB support — AWS Route 53, Cloudflare Load Balancing, NS1, and Azure Traffic Manager all offer this. Compare health check locations and routing policy options.
- Deploy origins in at least two regions before configuring GSLB — there's nothing to fail over to otherwise.
- Configure health checks at the provider level, pointing to a meaningful application endpoint.
- Set DNS TTLs low (30–60s) on your GSLB records. Keep TTLs higher on non-GSLB records to reduce resolver load.
- Test failover deliberately. Block traffic to one origin (iptables drop, security group deny) and verify that DNS stops returning that IP within your expected window.
- Monitor your monitors. Set up independent external checks so you know when your health check configuration itself breaks.
Common Pitfalls
- Sticky sessions across regions. If your app requires session affinity, cross-region failover can break user sessions. Solve this at the application layer (distributed session store, JWT) before relying on GSLB.
- Certificate coverage. Make sure your TLS certificates are valid for all origin IPs or use a wildcard/SAN cert that covers all endpoints.
- Assuming low TTL = instant failover. Negative caching, resolver non-compliance, and OS-level DNS caches all create lag. Design your recovery time objective around 2–5× your TTL, not 1×.
Key Takeaways
- GSLB routes DNS responses based on health and location; anycast routes DNS queries to the nearest nameserver — they solve different problems and work together.
- Health checks are the failure point most teams underinvest in. Check from multiple locations, check meaningful endpoints, and calibrate thresholds to avoid flapping.
- TTL, session handling, and TLS scope all need to be solved before GSLB failover works reliably in production.
- Test failover under realistic conditions before you need it — simulated failures are far cheaper than discovering gaps during an incident.